Threatium / Cyber defense & digital investigations

Beyond the Threat. Into the Evidence.

We uncover what happened. We investigate what matters. We help you take back control.

Threatium is an independent team of cybersecurity and digital forensics specialists with over 15 years of experience investigating digital incidents, recovering critical information, analyzing malicious software, and tracing complex cyber threats.

Threatium badge: a shield with the letter T over a world map of threat activity
  • 15+ years of experience
  • Specialized digital investigations
  • Evidence-driven analysis
  • Malware analysis
  • Cyber threats
  • Vulnerabilities & exploits
  • AI security
  • Practical defense
  • Security news
  • User awareness

Intelligence Meets Investigation.

A specialized team. A forensic mindset. A commitment to understanding the truth behind digital incidents.

Threatium was built around a simple principle: every digital incident leaves traces. Finding them requires more than automated security tools. It demands technical expertise, investigative thinking, and a deep understanding of how systems, software, and cyber threats operate.

With more than 15 years of practical experience, our specialists work across digital forensics, malware investigation, infrastructure security analysis, and blockchain transaction tracing. We combine the defensive mindset of a Blue Team with the precision of digital forensic investigation.

Our approach is independent, analytical, and evidence-driven.

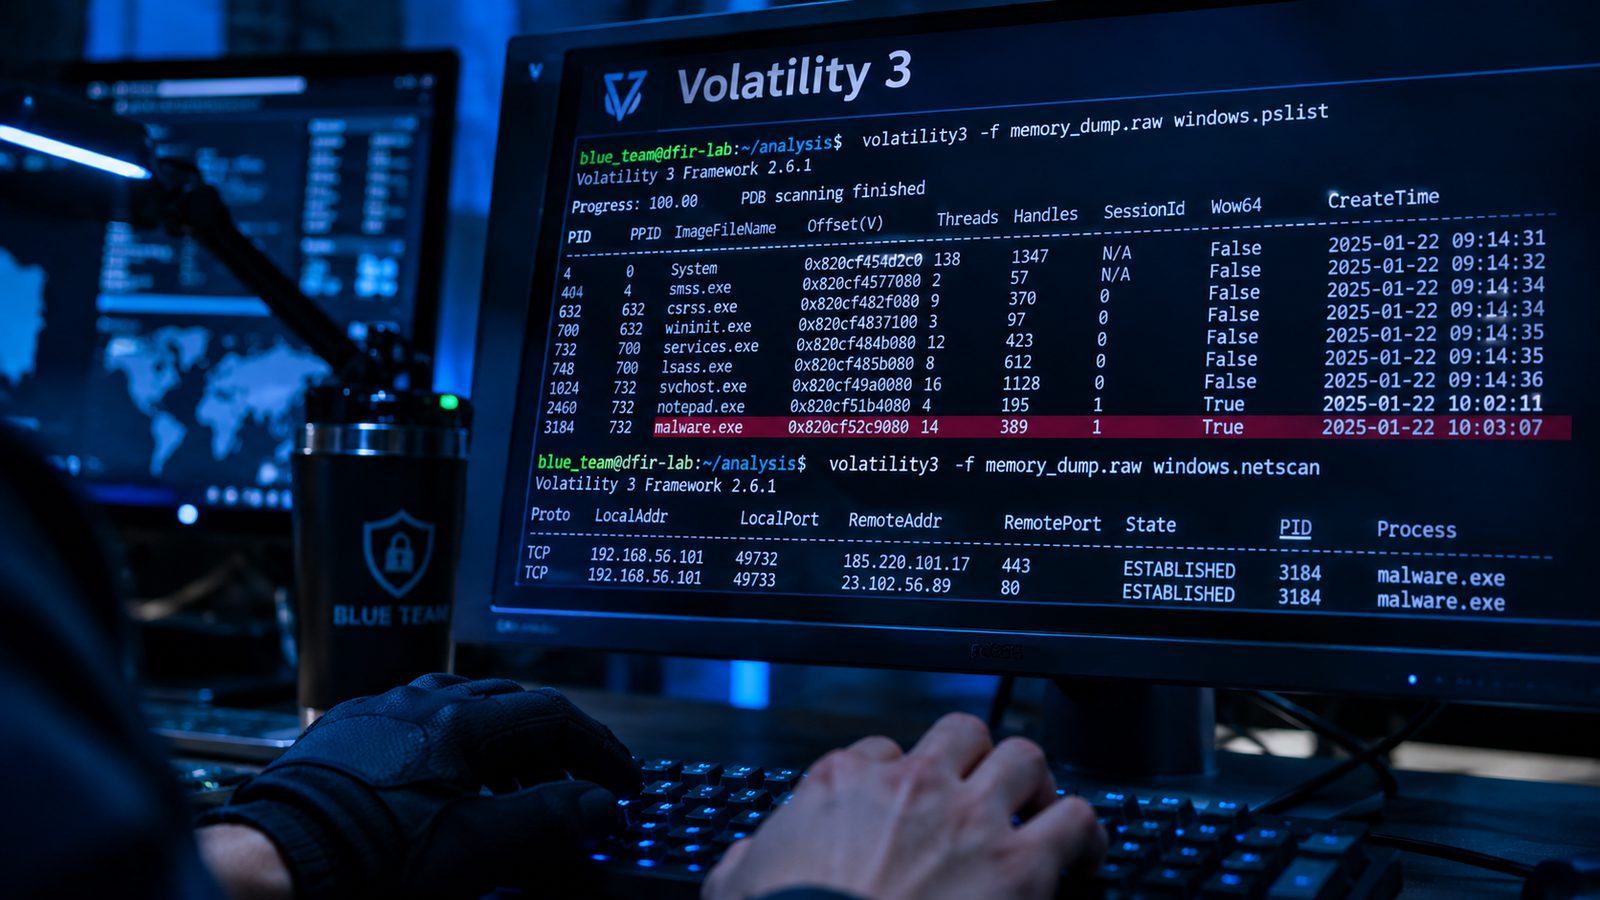
Analyst reviewing a memory dump process list in a terminal

Evidence over assumptions.

We follow the data, examine the artifacts, and build conclusions from verifiable technical findings.

Precision over noise.

We focus on relevant indicators, meaningful patterns, and the technical details that explain an incident.

Knowledge through investigation.

Every investigation contributes to a deeper understanding of evolving threats and defensive strategies.

Complex Threats. Focused Expertise.

From forensic evidence preservation to sophisticated malware investigations, Threatium delivers specialized technical analysis across critical areas of cybersecurity.

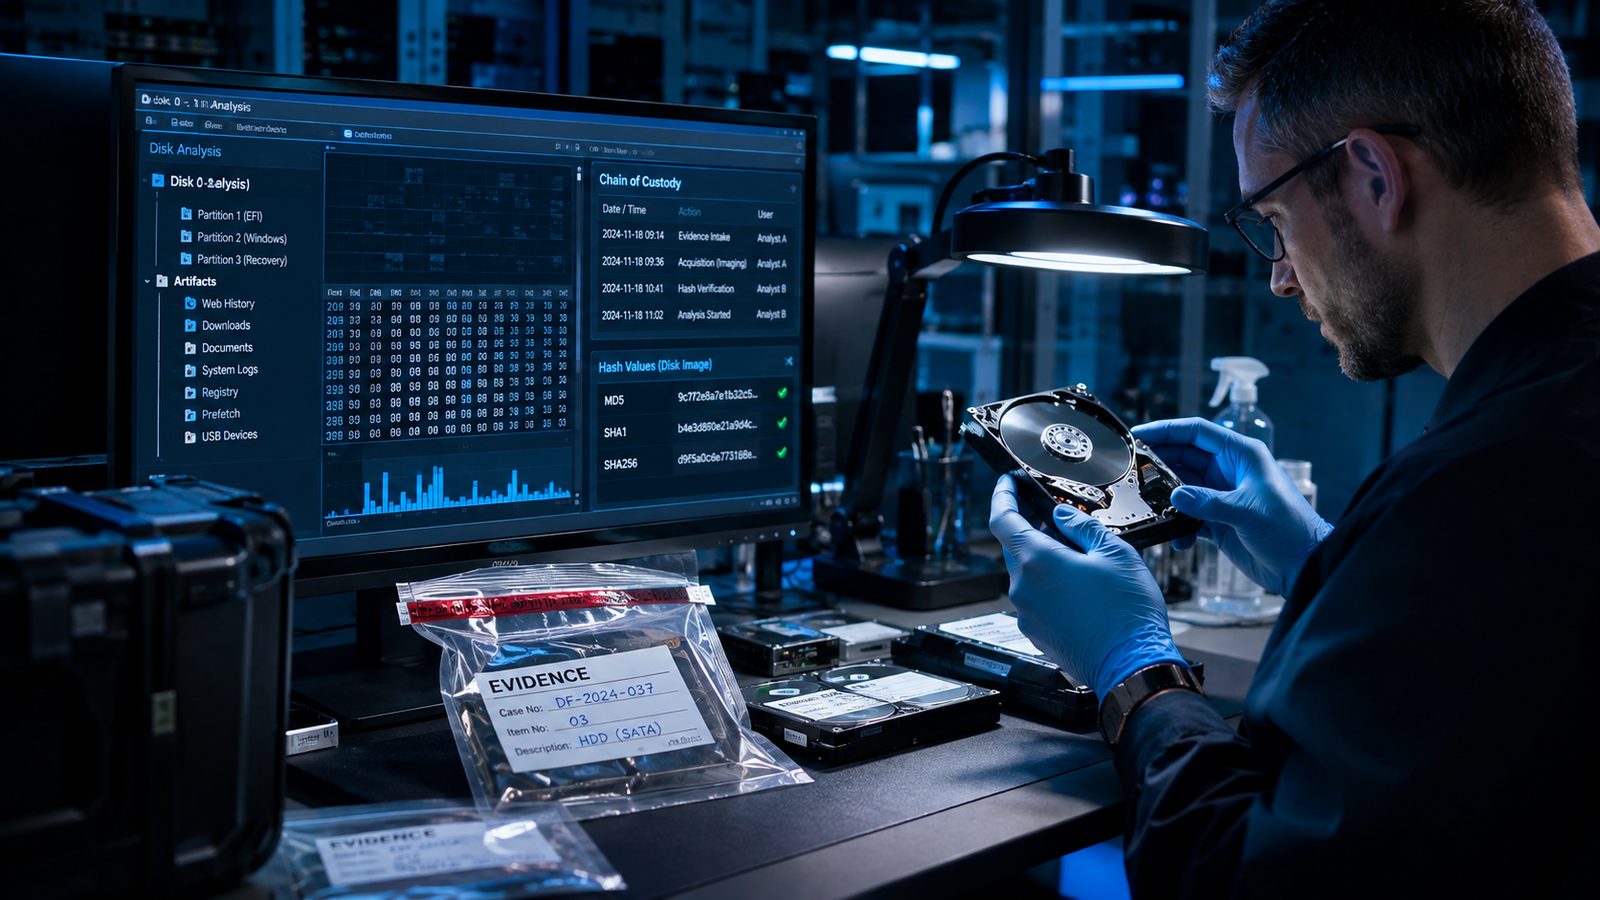
Examiner in gloves holding a hard drive next to a sealed evidence bag

Digital Forensics & Evidence Preservation

Every byte can tell a story.

We identify, preserve, examine, and analyze electronic data to reconstruct digital activity and uncover relevant evidence. Our work focuses on maintaining data integrity, examining digital artifacts, and producing structured technical findings that support further investigation.

  • Digital evidence acquisition
  • Disk imaging
  • File system analysis
  • Metadata examination
  • Forensic artifact analysis
  • Evidence integrity verification
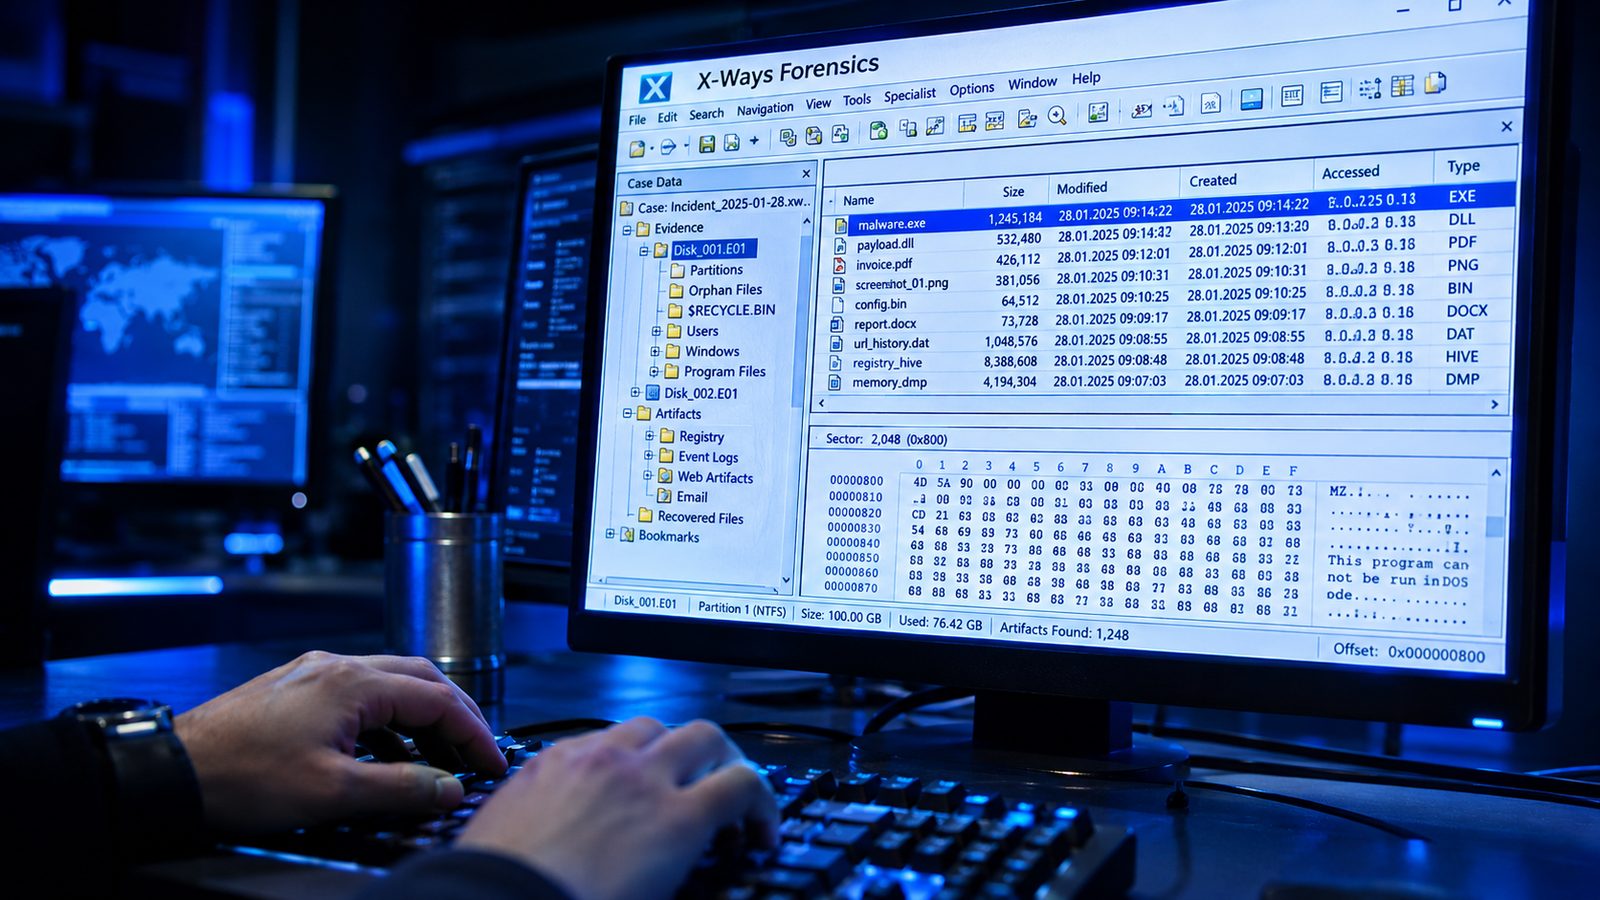
Forensic software listing recovered and orphaned files from a disk image

Deleted Data & File Recovery

Deleted does not always mean gone.

Accidental deletion, corrupted file systems, and damaged storage structures can result in the loss of valuable information. We investigate storage media and file system artifacts to assess recovery possibilities and attempt to retrieve deleted or otherwise inaccessible data.

Recovery depends on the condition of the storage device, the file system, and whether the original data has been overwritten.

  • Deleted file recovery
  • File system reconstruction
  • Storage media analysis
  • Data carving
  • Partition analysis
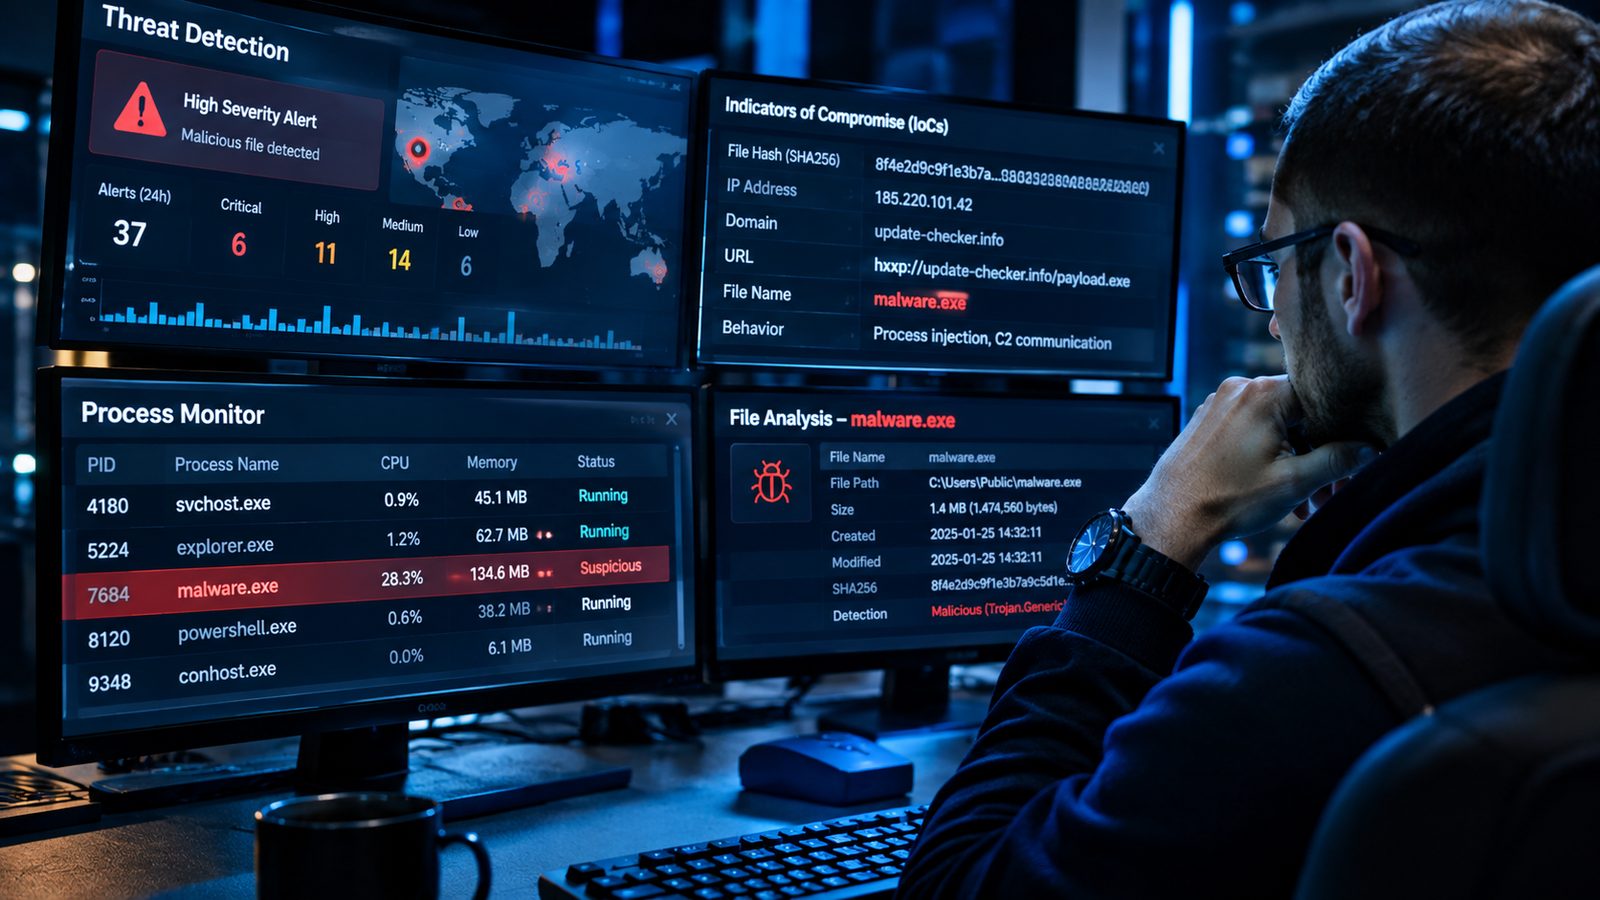
Analyst studying a threat detection dashboard with a flagged malicious process

Malware Analysis & Reverse Engineering

Understand the code. Expose the threat.

Malicious software is designed to operate unnoticed, manipulate systems, steal information, or establish unauthorized access. We analyze suspicious executables, scripts, and system artifacts to understand malware behavior, identify indicators of compromise, and investigate potential persistence mechanisms.

  • Static malware analysis
  • Dynamic malware analysis
  • Binary reverse engineering
  • Behavioral analysis
  • YARA-based detection
  • Indicators of compromise
Corridor between server racks in a data center

Server & Infrastructure Incident Investigation

When infrastructure is compromised, answers matter.

We investigate suspicious activity affecting servers, network services, and business-critical infrastructure. Our analysis focuses on identifying possible entry points, examining logs and system artifacts, reconstructing attack timelines, and determining the potential scope of compromise.

  • Server compromise investigation
  • Log analysis
  • Attack timeline reconstruction
  • Unauthorized access analysis
  • Network forensics
  • Root cause analysis
A shield and padlock over a network of connected nodes

Cryptocurrency Theft & Blockchain Investigations

Follow the transactions. Uncover the connections.

We analyze publicly available blockchain data to trace transaction flows, identify relevant wallet relationships, and document potential movement of stolen cryptocurrency. Our findings can support further investigation and provide structured information for legal professionals, exchanges, or competent authorities.

Blockchain tracing does not guarantee identification of an individual or recovery of stolen assets.

  • Blockchain transaction tracing
  • Wallet activity analysis
  • Fund flow mapping
  • On-chain intelligence
  • Transaction pattern analysis

From Digital Traces to Actionable Intelligence.

Every investigation begins with questions. Our methodology is designed to transform fragmented technical evidence into a coherent understanding of an incident.

Identify

Understand the incident, define the investigation scope, and identify relevant systems, data sources, and potential evidence.

Preserve

Acquire and safeguard relevant digital evidence using appropriate forensic procedures and integrity verification methods.

Analyze

Examine digital artifacts, system activity, malicious software, logs, network records, or blockchain transactions to identify meaningful findings.

Correlate

Connect technical indicators, reconstruct event sequences, and distinguish verified evidence from assumptions.

Report

Present findings in a structured, understandable format, including technical observations, relevant evidence, limitations, and recommended next steps.

Our objective is not simply to detect anomalies. It is to understand their significance.

Threats Evolve. So Does Our Understanding.

New malware variants, attack techniques, infrastructure vulnerabilities, and fraudulent schemes continue to challenge traditional security approaches. At Threatium, we approach cybersecurity through continuous learning, technical research, and practical investigation.

Knowledge is one of the most effective layers of defense.

Our areas of interest

  • Malware behavior & emerging threats
  • Indicators of compromise (IoCs)
  • Attack techniques & MITRE ATT&CK
  • Endpoint & server security
  • Network traffic & anomaly analysis
  • Blockchain-based criminal activity
  • Digital forensic techniques

Cybersecurity Knowledge Should Be Accessible.

Learn to recognize threats before they become incidents.

We believe cybersecurity awareness should extend beyond security professionals. Through our YouTube and Instagram channels, Threatium shares educational videos, practical demonstrations, and accessible explanations of real-world cyber threats.

Our goal is to help individuals understand how attacks work, recognize suspicious behavior, and take meaningful steps to protect their own devices and digital identities.

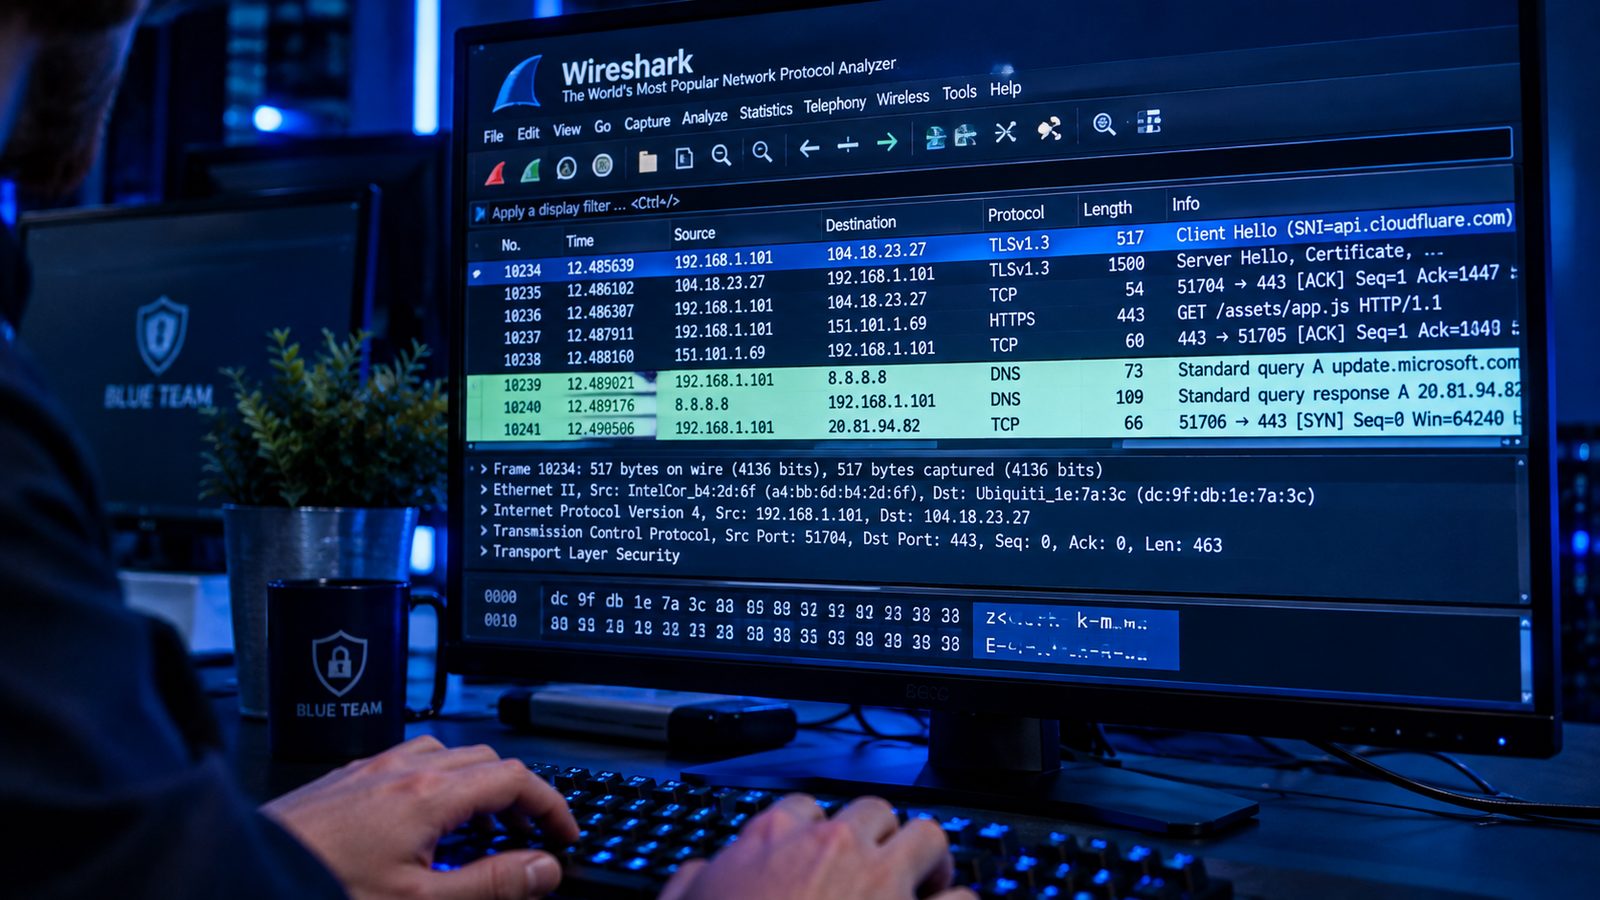
Blue Team workstation showing captured network traffic
Topics we cover: malware analysis, cyber threats, vulnerabilities and exploits, AI security, practical defense, security news, user awareness

What you'll learn

Recognize suspicious files

Understand common warning signs of malicious executables, scripts, and unexpected downloads.

Protect your devices

Learn practical techniques for improving operating system security, managing updates, and reducing exposure to common threats.

Understand malware behavior

Explore how malicious software operates, what indicators it may leave behind, and how analysts investigate suspicious activity.

Identify online scams

Learn to recognize phishing attempts, fraudulent websites, impersonation, and cryptocurrency-related scams.

Explore digital forensics

Discover the tools, techniques, and investigative thinking used to examine digital evidence.

Better awareness. Stronger defenses. Safer digital lives.

Every Digital Incident Has a Story. Let's uncover yours.

Whether you're dealing with suspicious system activity, missing data, a compromised server, or an unexplained cryptocurrency transaction, understanding the facts is the first step forward.

contact@threatium.si